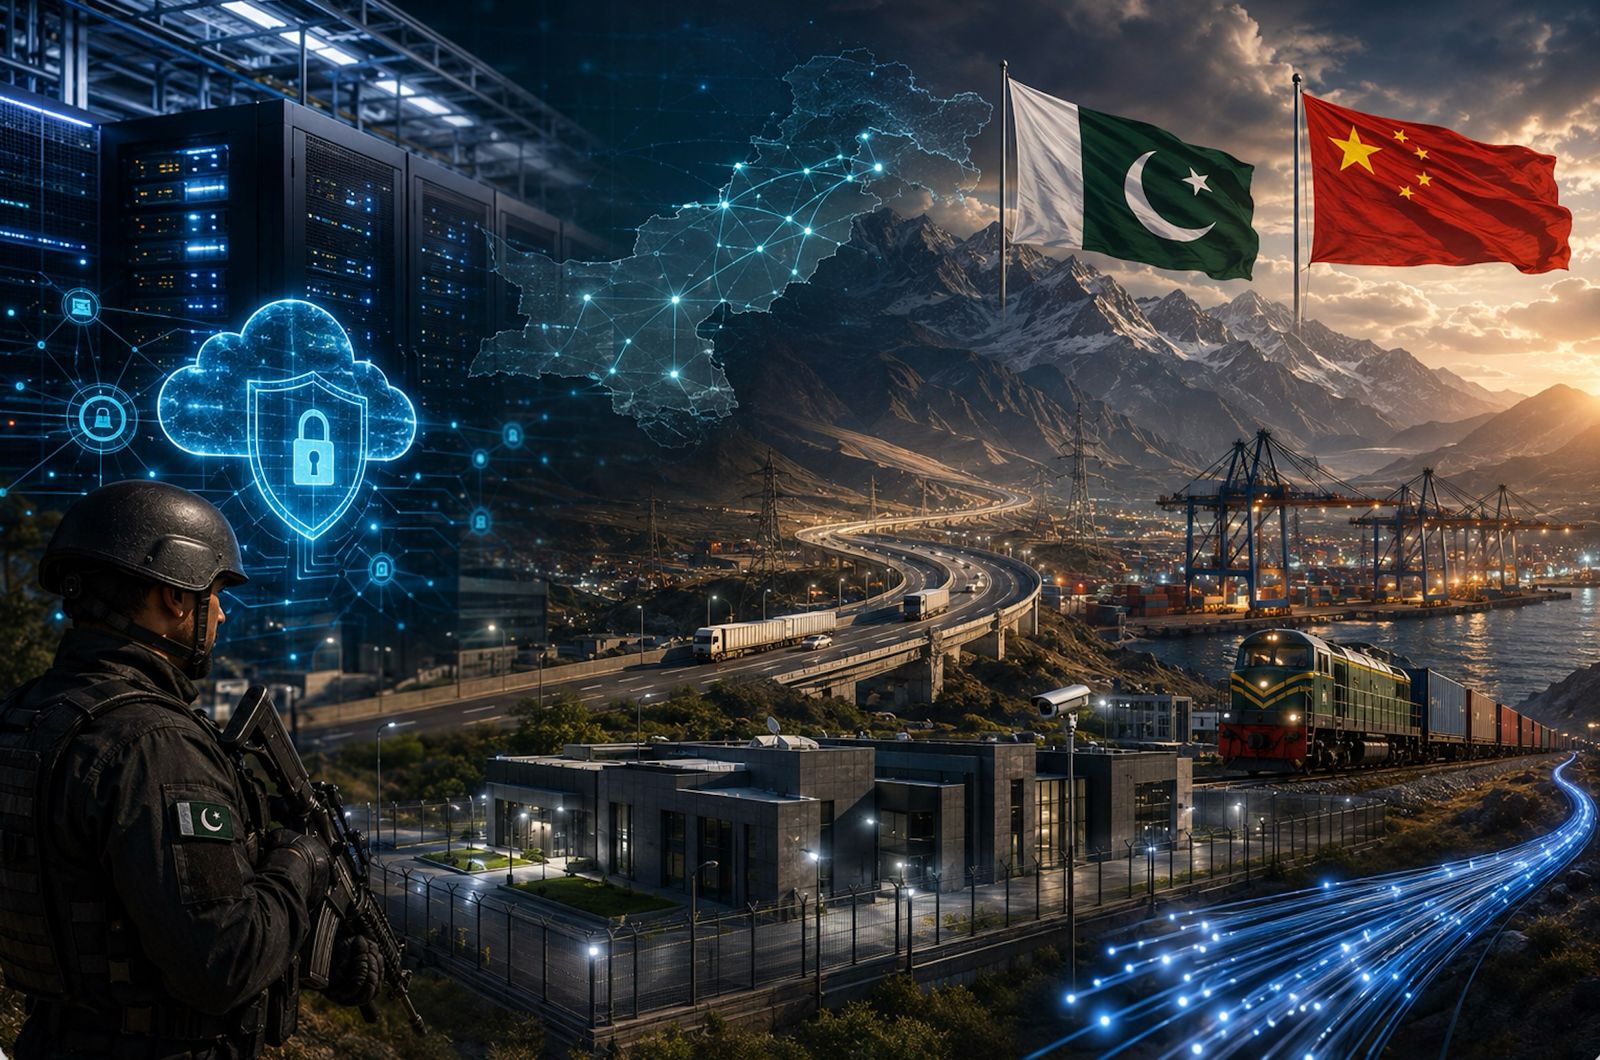
The China Pakistan Economic Corridor (CPEC) is the strategic pivot of Pakistan-China relations. The second phase of CPEC 2.0 aims to extend the strategic partnership from infrastructural development, land and energy corridors, ports, power plants and highways into a soft digital architecture focused on connectivity, governance and services. This main transformation with the CPEC project can be understood through the evidence of the Digital Silk Road (DSR). Pakistan recently inaugurated the first AI sovereign data centre, known as the Sky47 Karakoram-01 facility, in Islamabad. This AI data centre is the first built infrastructure platform for sovereign cloud, AI acceleration, and enterprise transformation. Two more centres will be established at Port Qasim in Karachi and in Lahore in collaboration with the Chinese tech firm, ZTE Corporation which deals with 5G infrastructure, telecommunications, and mobile devices. The Digital Silk Road intends to build Chinese-backed centres, cloud computing networks, and cross-border fibre optic networks across Pakistan. The extension of strategic partnership from defence and economy to the digital ecosystem has brought new security concerns for Pakistan and China. Therefore, security is still the key pillar constraining and driving CPEC 2.0.
The contemporary developments can be understood through the framework of security. The security apparatus of CPEC 1.0 was built under the Special Security Divisions (SSDs) comprising of military personnel and security forces for the safety and protection of Chinese engineers, construction sites, energy installations, physical assets, and transportation routes. CPEC 1.0 was intensely targeted by the militant groups, including Tehrik-i-Taliban Pakistan (TTP) and the Baloch Liberation Organisation (BLA). During 2004-2024, around 36 attacks took place against Chinese nationals. However, the nature of digital security is entirely different from kinetic threats, as data centres contain high-density physical hardware, servers, cooling grids, and fiber link connections along with telecom traffic, AI workloads, hosting of sensitive data, and financial records. The security of these physical and digital installations requires an integrated security network that is based on integrated cybersecurity protocols and physical security. This approach can protect them from militants and external state actors that intend to sabotage and breach the security controls.
Therefore, one of the main challenges to the Digital Silk Road is the security of digital ground assets. The physical vulnerability of overland fibre optic cables stretching around 822 kilometers between Pakistan and China, running through highly volatile and risky zones, passing from Khunjerab Pass down through Gilgit-Baltistan and Khyber Pakhtunkhwa. In order to protect against any attack by TTP, BLA and other militant groups, ground deployment of security forces is essential. Moreover, security protocols for data centres, cellular towers, and submarine landing stations are significant. The digital Silk Road is not abstract; rather, it relies on sea cables. For example, PEACE (Pakistan & East Africa Connecting Europe) Cable, built by China’s Hengtong/HMN Tech. It lands in Karachi and Gwadar and connects overland to China via the Karakoram Highway. In this context, militant groups operating in coastal Baluchistan have already targeted land-based CPEC assets and Chinese personnel. Extending that threat vector offshore, such as targeting shallow-water landing stations or near-shore conduit pipes, is a natural evolution of asymmetric warfare. In addition, though submarine cables are thousands of miles in Deep Ocean but the chokepoint dilemma persists, as they are highly vulnerable in the shallow waters near the coast and the landing stations at the beach where the sea cable is linked with the terrestrial network.
Another challenging domain for Pakistan is data sovereignty. One of the main objectives that Pakistan intends to achieve from these developments in digital sovereignty is based on the principle that individual nations must possess absolute authority over the digital infrastructure and data flows within their borders. By deploying localised, Tier III/IV data center campuses, Chinese technology firms enable Pakistan to achieve true data localisation. Rather than routing sensitive domestic traffic or public sector workloads through third-party foreign servers, Pakistan can host its sovereign data within its own geographic boundaries. However, it will create concerns among the regional states and Western powers regarding Pakistan’s heavy reliance on Chinese hardware.
Pakistan’s digital integration into the data landscape also serves as an operational test case for China’s Global Security Initiative (GSI). The GSI, which Beijing introduced in April 2022 to support comprehensive, unconventional security frameworks, highlights the interdependence of state stability, economic growth, and digital security. In reality, Chinese technology companies that supply data centre solutions to Pakistan export a whole operational security ecosystem rather than just server racks. It includes the use of monitoring systems based on artificial intelligence for the protection of computers from any external intrusion. The Robust Redundancy Networks that are designed for a backup communication system in case of any disruption in the physical infrastructure. The connectivity of the Khunjerab-Rawalpindi cable directly with submarine cable landing stations for the purpose of data preservation is one example. Moreover, China is facilitating Pakistan in developing technical standardisation through capacity building, digital governance, and ICT infrastructure. Pakistan is among 29 founding members of World Artificial Intelligence Cooperation Organization (WAICO). This Chinese-led initiative was launched on 16th July 2026, intending to build an inclusive AI system. The following conference in Shanghai on 17th July 2026 also provides a leading insight that AI is not solely a technological domain for states; rather, it has become a key pillar of geopolitical and strategic competition.
Far from shifting CPEC away from hard geopolitical realities toward pure economic modernisation, the emerging China–Pakistan digital alliance demonstrates that security remains the foundational pillar of the relationship re-engineered from the physical protection of asphalt to the strategic defence of algorithms and data flow. Pakistan rigorously needs to develop protocols for data architecture, including institutionalising data auditing, secrecy, and efforts to have sustainable and consistent digital nodes. In CPEC 1.0, maritime security focused primarily on protecting surface trade and Gwadar Port, leading to the Pakistan Navy raising Task Force 88 and Coastal Security forces. In CPEC 2.0, maritime security must expand into undersea surveillance and critical seabed infrastructure protection (CSIP). In addition, data centres are not passive computing hubs; they are strategic outposts designed to maintain the continuous, uninterrupted flow of commerce, governance, and intelligence between Beijing and Islamabad.
The security dimension of CPEC 2.0 also extends to the Digital Silk Road, as digital infrastructure is embedded within Pakistan’s broader security environment. While discussions of the Digital Silk Road often focus on cybersecurity, data governance, and technical standardisation, physical security threats remain equally relevant. Fibre-optic networks, telecommunications facilities, data centres, and other critical digital infrastructure may be vulnerable to sabotage or disruption by militant groups operating in regions where CPEC projects are located. Such threats reinforce the need for a comprehensive security framework that integrates physical protection, cyber security, and resilient technical standards. Consequently, security in CPEC 2.0 should be understood as a multidimensional concept encompassing both traditional threats posed by militant groups and non-traditional risks associated with the digital domain.